SaltStack Config vs. Ansible Tower: A Comparison of Two Powerful Configuration Management Solutions

SaltStack Config and Ansible Tower are two powerful configuration management and infrastructure automation tools that cater to the needs of DevOps teams across the globe. While SaltStack Config is an open-source solution, Ansible Tower is the commercial, enterprise-ready version of Ansible Open Source. In this blog post, we will compare SaltStack Config and Ansible Tower in terms of architecture, ease of use, scalability, and features to help you make an informed decision on which tool is best suited for your requirements. ...
SaltStack Config vs. Ansible Tower: A Comparison of Two Powerful Configuration Management Solutions

SaltStack Config vs. Ansible Open Source: A Technical Comparison

SaltStack Config and Ansible Open Source are two popular configuration management and infrastructure automation tools used by DevOps teams across the globe. Both solutions have their own unique set of features, advantages, and drawbacks. In this blog post, we will compare SaltStack Config (formerly known as Salt) and Ansible Open Source in terms of their architecture, ease of use, scalability, and community support, to help you make an informed decision on which tool is best suited for your needs. ...

SaltStack Config vs. Ansible Open Source: A Technical Comparison

A Step-by-Step Guide to Convert Native Cloud Virtual Machines to On-Prem vSphere with VMware Converter

Migrating virtual machines (VMs) from a cloud environment to an on-premises VMware vSphere infrastructure can be a daunting task. However, with the right tools and processes in place, it can be a seamless and efficient process. One such tool is the VMware Converter, which enables users to convert native cloud VMs\physical servers to vSphere machines. In this blog post, we will discuss the benefits and challenges of converting cloud VMs and provide a step-by-step guide for using VMware Converter to achieve this goal. ...

A Step-by-Step Guide to Convert Native Cloud Virtual Machines to On-Prem vSphere with VMware Converter

Overview of deploying a 3 tier app in vRA 8, Terraform, and Ansible

Introduction When it comes to deploying a three-tier application in Google Cloud Platform (GCP), there are several tools available, including vRealize Automation (vRA) 8, Terraform, and Ansible. Each tool has its own strengths and weaknesses, and choosing the right one for your project depends on several factors. In this blog post, we will compare these three tools and discuss how vRA 8 stands out as the best option for deploying a three-tier application in GCP. ...

Overview of deploying a 3 tier app in vRA 8, Terraform, and Ansible

Deploying a 3 tier app in GCP from Ansible

Ansible is an open-source automation tool that allows you to automate configuration management, application deployment, and task automation. In this blog post, we will explore how to deploy a three-tier application in Google Cloud Platform (GCP) using Ansible. If you prefer other tooling, I also covered deploying the same 3 tier app in GCP from Terraform and from vRA. GCP and Ansible Overview GCP Overview Google Cloud Platform (GCP) is a suite of cloud computing services offered by Google. It provides a wide range of services such as virtual machines, storage, and networking, among others, that can be used to deploy and run applications in the cloud. One of the advantages of using GCP is its high availability and scalability, which makes it an excellent option for deploying enterprise-grade applications. ...

Deploying a 3 tier app in GCP from Ansible

Deploying a 3 tier app in GCP from Terraform

Deploying a three-tier application using Terraform is a popular approach because it provides infrastructure-as-code benefits. Terraform is an open-source infrastructure-as-code tool that allows you to define, configure, and manage infrastructure in a declarative language. In this blog post, we will explore how to deploy a three-tier application in Google Cloud Platform (GCP) using Terraform. GCP and Terraform Overview GCP Overview Google Cloud Platform (GCP) is a suite of cloud computing services offered by Google. It provides a wide range of services such as virtual machines, storage, and networking, among others, that can be used to deploy and run applications in the cloud. One of the advantages of using GCP is its high availability and scalability, which makes it an excellent option for deploying enterprise-grade applications. ...

Deploying a 3 tier app in GCP from Terraform

Deploying a 3 tier app in GCP from vRA

Deploying a three-tier application is a common task for many organizations, and as more companies move to the cloud, it’s essential to understand how to deploy such applications in the cloud environment. In this blog post, we will explore how to deploy a three-tier application from vRealize Automation 8 in Google Cloud Platform (GCP) using a blueprint. GCP and vRA 8 Overview GCP Overview Google Cloud Platform (GCP) is a suite of cloud computing services offered by Google. It provides a wide range of services such as virtual machines, storage, and networking, among others, that can be used to deploy and run applications in the cloud. One of the advantages of using GCP is its high availability and scalability, which makes it an excellent option for deploying enterprise-grade applications. ...

Deploying a 3 tier app in GCP from vRA
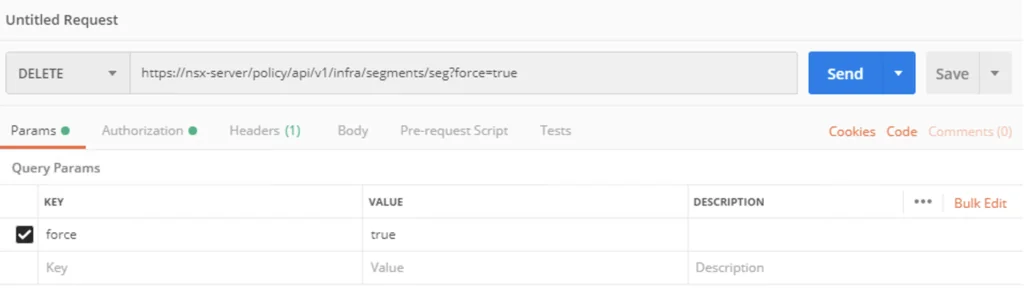
API request setup for forcibly deleting an NSX-T 3 segment using Postman.

How to forcibly delete an NSX-T 3 Segment

I recently ran in to a problem where I couldn’t delete an NSX segment so I went exploring the API. The API guide can be found here The method used is delete policy/api/v1/infra/segments/{segment-id}?force=true It would look like this in Postman: To list the segments we can use a get request towards /policy/api/v1/infra/segments/ ...

How to forcibly delete an NSX-T 3 Segment

Removing NSX stale packages from ESXi host

Important safety update (August 25, 2026): Do not manually remove NSX VIBs with esxcli software vib remove. Broadcom documents that this method is unsupported and can cause loss of management or workload networking. The executable removal guidance previously shown on this page has been removed. Use the current follow-up instead: Safely Removing Stale NSX VIBs from an ESXi Host. It starts with the NSX Manager removal workflow and covers the narrower stale-package condition where Broadcom directs administrators to use nsxcli -c del nsx while the host is in maintenance mode. ...

 · Updated  · 
Removing NSX stale packages from ESXi host
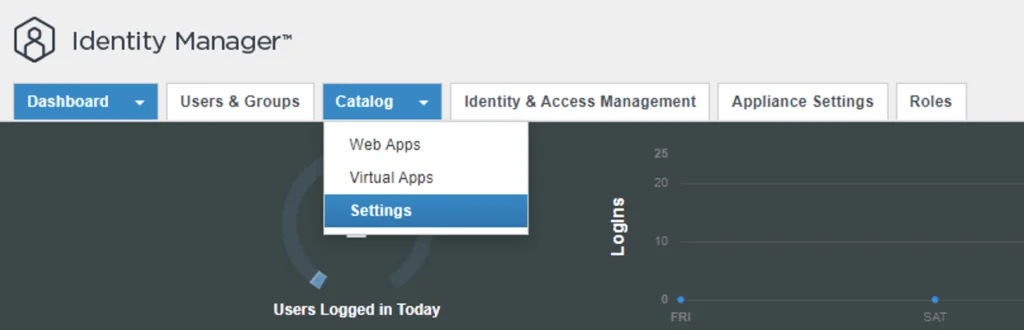
Identity Manager dashboard showing Catalog and Settings options.

Configure NSX-T to use vIDM as authentication

I needed to create a few additional accounts in NSX-T for outside sources. Instead of creating individual accounts I wanted to use the existing ones from AD. To get started we need to get the certificate from the vIDM server. Log on to the vIDM server as root and run the following: openssl1 s_client -connect <FQDN of vIDM host>:443 < /dev/null 2> /dev/null | openssl x509 -sha256 -fingerprint -noout -in /dev/stdin Next, create the OAuth client ID in vIDM. Log in to the vIDM UI as an administrator at https://<FQDN-of-vIDM-host>/SAAS/admin/app/page#!/dashboard, then navigate to Catalog -> Settings. ...

Configure NSX-T to use vIDM as authentication